@node.io
TikTok · Split screen
@node.io Why Is C SO Dangerous? #programming #coding #lowcode #Programming #computersciencemajor #techtoktips #c++

@node.io
TikTok · Split screen
@node.io Why Is C SO Dangerous? #programming #coding #lowcode #Programming #computersciencemajor #techtoktips #c++
Performance
Video #33053 · Split screen
[01]
The creator uses a bait-and-switch opening with a viral clip, then pivots to an educational explanation of why the C programming language is unsafe. He demonstrates a buffer overflow vulnerability by showing code that accesses an array out of bounds, compiles it, and shows the resulting crash. He then reframes the issue to explain how such vulnerabilities occur in real-world applications through user input, concluding that C's lack of built-in safety checks is the root cause.
[02]
[03]
 351.2K88.3×Greenscreen legacy tech system breakdown@maxxrosenblum · Breakdown
 234.3KTwo-step guide to learn cybersecurity@node.io · Breakdown
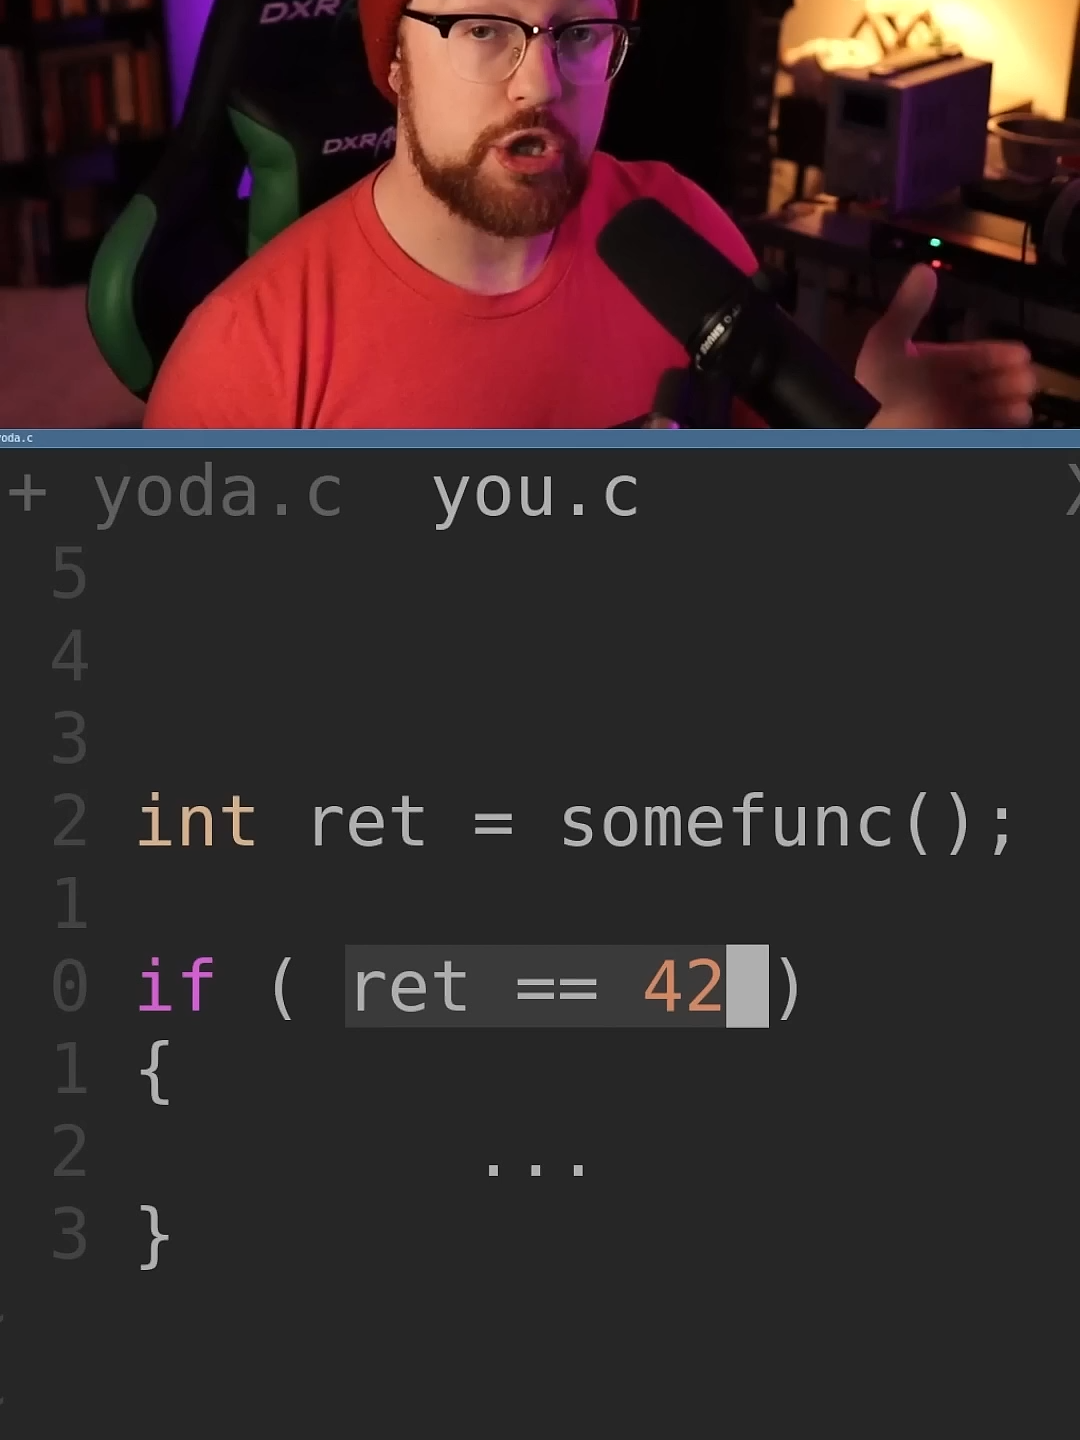 92K2.1×Explains Yoda notation coding trick@node.io · Good vs Bad
 250.2K1.8×Creator explains online security steps@covacut · Public Service Announcement
 552.1K120.3×Explaining a hidden financial crisis@maxxrosenblum · Breakdown
 1.8M17.1×Explaining security engineering through rap.@chrisjereza · Trendjacking
 118.8KWeekly security news roundup@wired · Headlines
 203.8K7.3×Creator defends a coding trend@angus.sewell · Hot Take
 68.9K2.1×Developer advice with whiteboard drawings@node.io · Tutorial / How To
 333.4K4.5×Reddit story illustrates SSN danger@guacandpico · Breakdown
 1.1M1.7×SQL tutorial using trap analogy@arrionknight · Tutorial / How To
 121.1K3.7×Sarcastic commentary on production code@node.io · Relatable Skit
[04]
[05]
What stops the scroll in the first 3 seconds
Title hook · 45%
HOW TO MAKE A GIRL LIKE YOU 😏❤️
Verbal hook · 50%
If you wanna make a girl like you No. Thank you.
Visual hook · 5%
An abrupt cut from a typical influencer-style video of a young woman in a room with LED lights to a male speaker in a studio setting with a code editor on screen, creating a strong pattern interrupt.
[07]
The promise the opener makes, and how the video pays it back
Hook
A pattern-interrupt that subverts the expectation of a preceding viral clip, immediately pivoting to the creator's own topic to capture attention through surprise.
Payoff
A concluding statement that generalizes the specific example into a universal principle, solidifying the lesson's importance and providing a satisfying 'aha' moment, followed by a direct call to action.
[08]
The structural pattern this video runs on
Framework
The High-Stakes Reframe
To demonstrate a hidden, dangerous flaw in a common system by starting with a simple, unbelievable example and escalating it to a real-world, high-stakes consequence.
The Core Thesis
Clearly and concisely state the central, often controversial, argument of the video, setting the viewer's expectation for the proof to come.
The Impossible Demonstration
Visually present a simple, concrete example that seems to break the rules of the system being discussed, serving as the primary piece of evidence.
The System's Failure
Showcase how the established safeguards or common knowledge fail to prevent the 'impossible' action, proving the initial thesis and creating a moment of surprise.
The Skeptic's Rebuttal
Acknowledge and voice a likely objection or question from the audience, building rapport and preemptively dismantling counter-arguments.
The High-Stakes Escalation
Reframe the simple demonstration within a real-world, high-stakes context, transforming a trivial example into a significant and dangerous problem.
Why Is C SO Dangerous? #programming #coding #lowcode #Programming #computersciencemajor #techtoktips #c++
title · beginning
HOW TO MAKE A GIRL LIKE YOU 😏❤️
contextual · beginning
Guaranteed to work ;)
If you wanna make a girl like you No. Thank you. Now the reason that c is an unsafe language is because you can do things like this. The integer array has forty ninety six bytes allocated to it, but I can index into and set the seven thousandth byte in that array and then also access that memory. And the crazy part is that the GCC compiler doesn't care. I can literally do g c c dot no bad bad dot c. The program doesn't care, and it just creates a crashing state. No, obviously, you're probably thinking, I know you worse. I was too. You know, why would I ever code like this? I would never select the seven thousandth element. Well, what if, for example, we gave the power to the user to do this over the Internet? Index I come in from the network that equals 7,000, and then we set array of I equal to some value. This is how the majority of all memory corruption bugs happen. You have an array, you have an access or a read outside of that array, and c has no way to check it. Subscribe for more